
Stellar's smart contract platform Soroban differs from EVM in authorization, storage with TTL expiry, cross-contract calls, and asset handling. Security audits must check both the application logic and these platform-specific behaviors. Certora outlines the key audit considerations for Soroban builders.
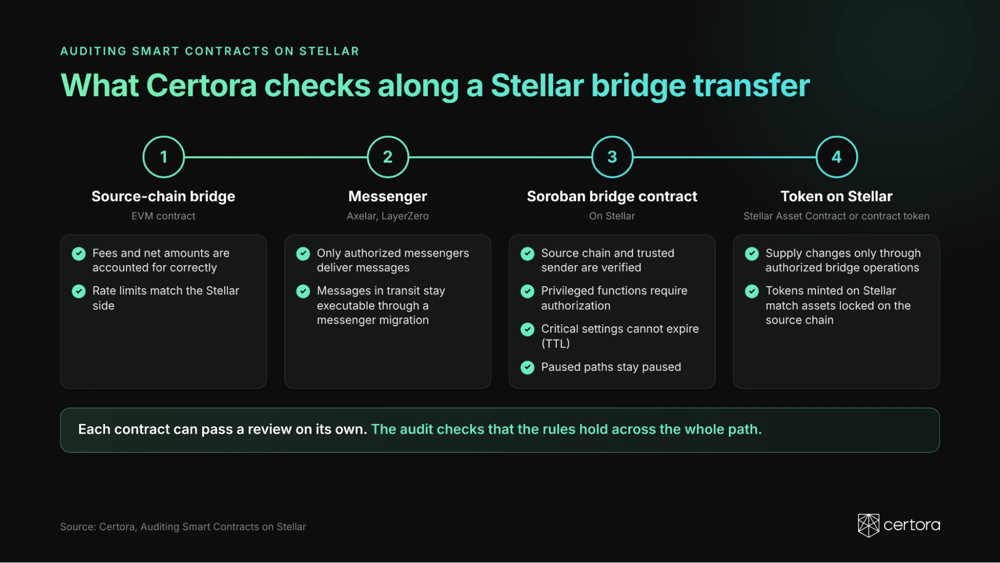
Stellar's smart contract platform Soroban handles authorization, data storage, contract calls, and assets differently from Ethereum. A security audit on Soroban has to verify both an application's business logic and how it uses these platform features correctly. Key audit considerations include how authorization propagates across contract calls, whether critical state can expire via Soroban's TTL model, how assets flow between contracts and the native Stellar Asset Contract, and how bridges maintain consistency between chains. Cross-chain applications introduce additional complexity: a valid transfer on one chain can become stranded if the corresponding message fails on Stellar. Certora is one of eight firms in the Soroban Security Audit Bank, which funds audits for Stellar Community Fund projects. The guide covers patterns from bridges, oracles, tokens, and access control audits.
